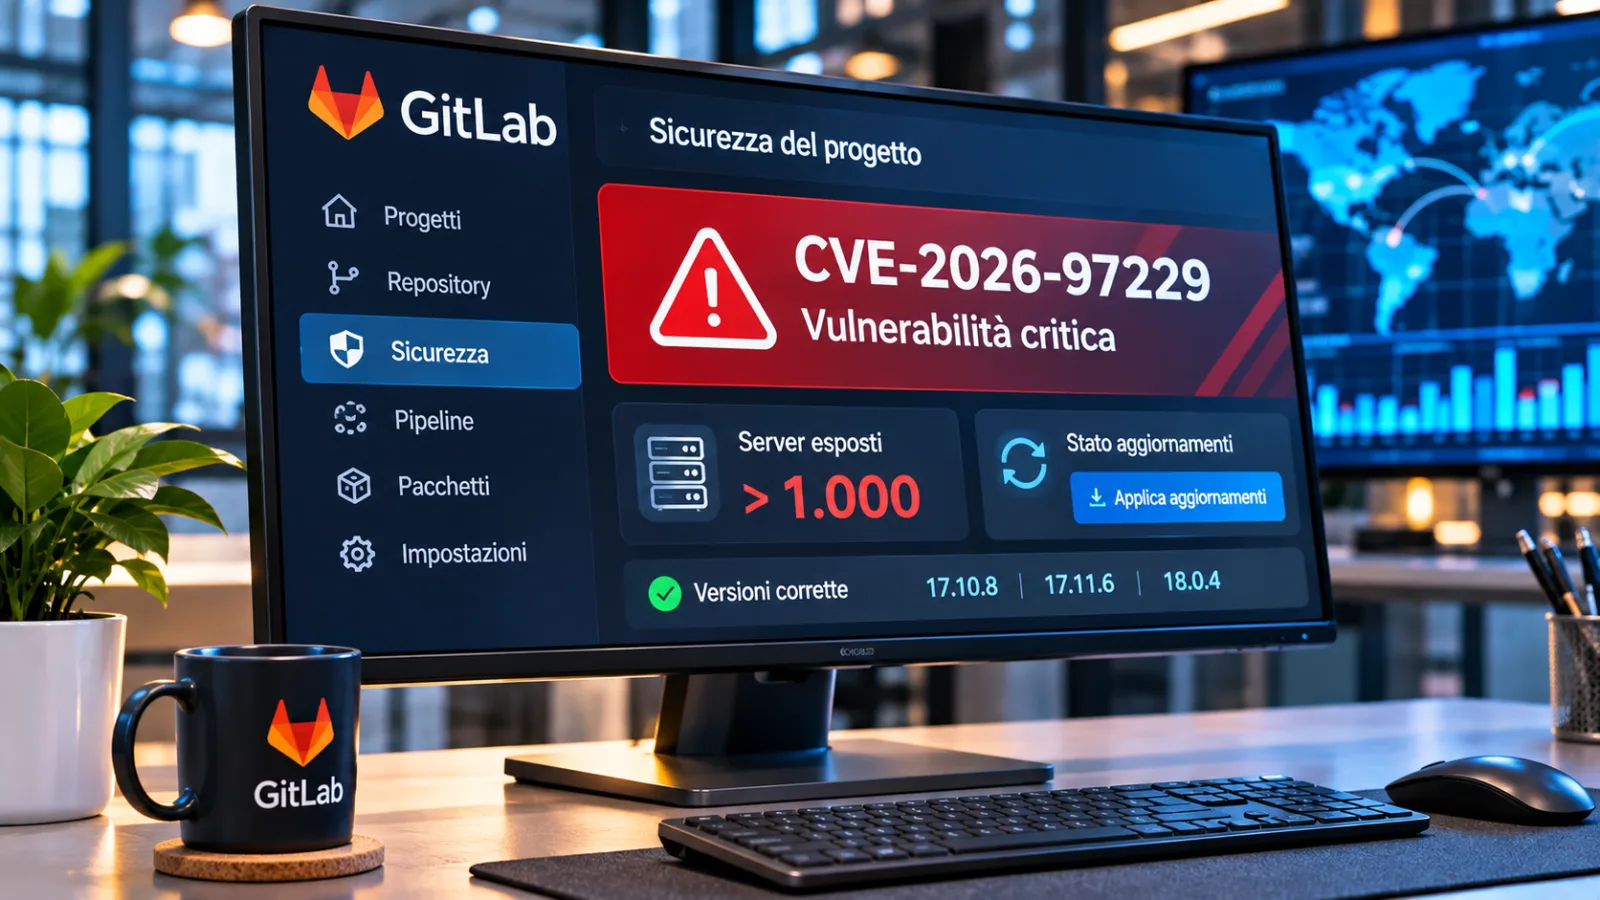
CVE-2026-97229 GitLab Vulnerability Under Attack: Over 1,000 Servers Out of Patch
The GitLab vulnerability CVE-2026-97229 is already exploited in attacks: over 1,000 servers remain exposed. Here are the correct versions.
vulnerability GitLab CVE-2026-97229 - Over 1,000 GitLab servers exposed on the Internet remain unpatched for a maximum severity vulnerability previously exploited in remote code execution attacks. The flaw, identified asCVE-2026-97229, affects the regular expression compiler used in CI/CD pipelines. Even theCISAUS has confirmed ongoing attacks, placing the problem in the catalog of actively exploited vulnerabilities.
Over 1,000 servers exposed to GitLab vulnerability CVE-2026-97229
According to data released by Shadowserver over the weekend, more than 1,000 GitLab instances accessible from the Internet are still vulnerable to CVE-2026-97229, despite the fixes having been available for about three weeks. The data does not indicate that all these systems have been compromised: it identifies installations that are exposed and not updated in a period in which the vulnerability is already being exploited in real attacks.
The situation is particularly delicate for organizations that manage GitLab themselves. The platform hosts repositories and development processes, but in this case the weak point is the treatment of CI/CD pipeline configurations. The presence of a vulnerable version on an externally reachable server therefore requires timely verification.
How the flaw in the regular expression compiler works
CVE-2026-97229 arises from ainteger overflowin the CI/CD Regular Expression Compiler component, responsible for parsing and evaluating regular expressions present in pipeline configuration files. GitLab explained that insufficient validation of these expressions can, under certain conditions, allow an unauthenticated user to execute arbitrary code on the server through a specially constructed CI/CD setup.
The ability to execute code remotely without authentication distinguishes this flaw from a normal operational error: an attacker could directly target the vulnerable instance. However, the available information does not allow us to state that every non-updated installation has already been violated, nor to attribute consequences to the attacks beyond the code execution mechanism described.
The correct versions and installations that need to take action
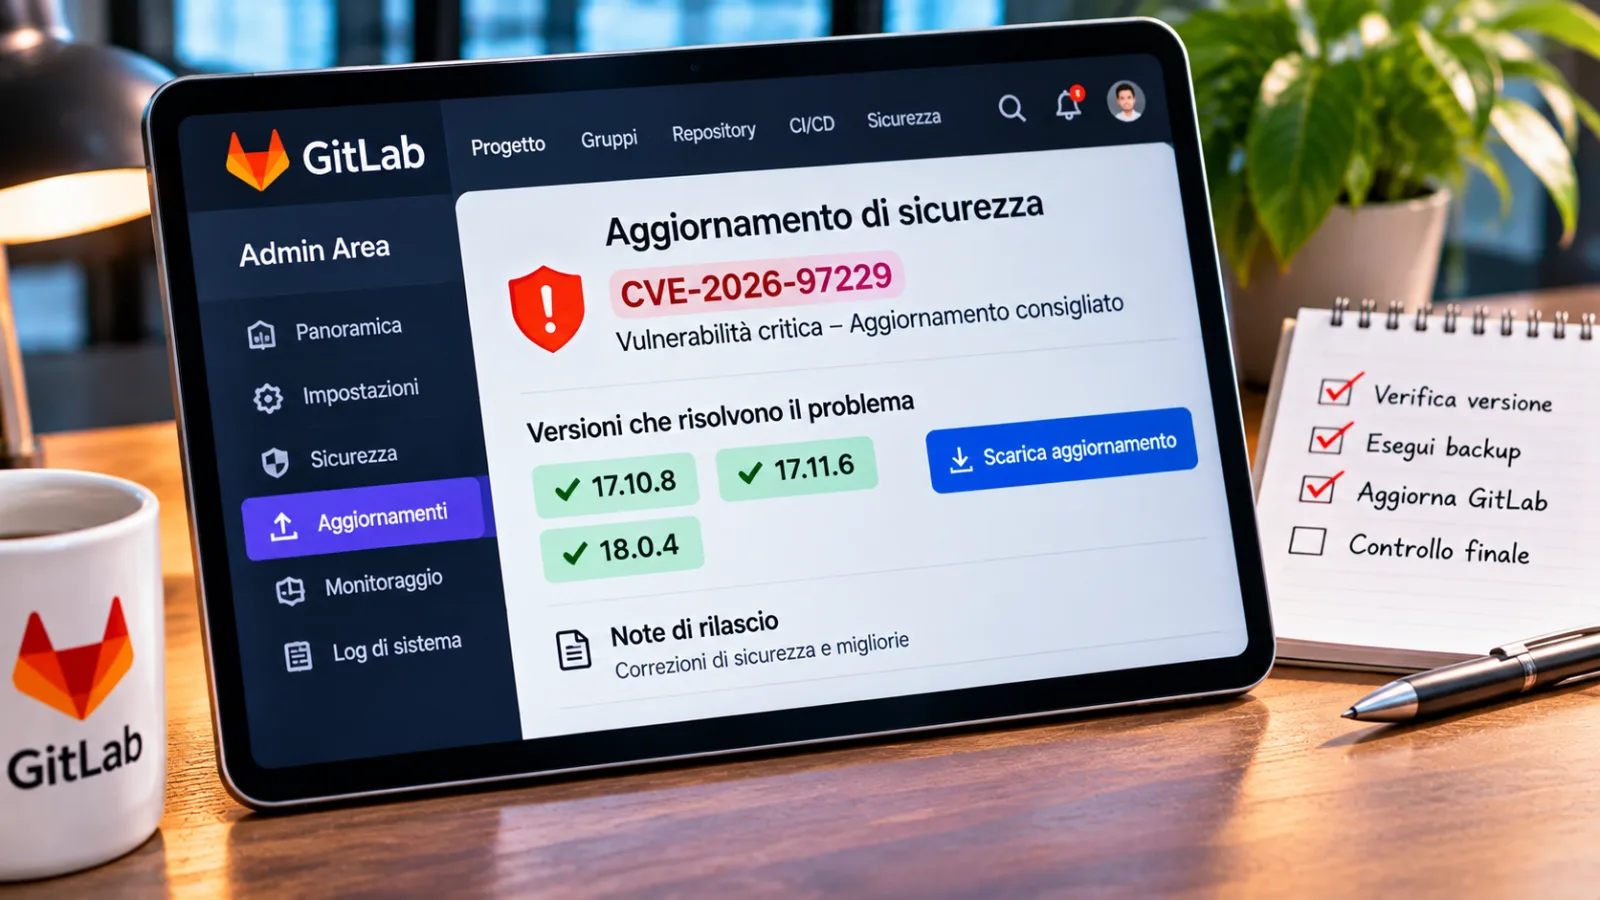
The company recommended that administrators of all self-managed installations immediately switch to one of the patched versions appropriate for their branch.
GitLab also clarified thatGitLab.com already uses a correct versionand that customersGitLab Dedicatedthey do not have to carry out interventions. The urgency therefore concerns above all those who directly maintain their own GitLab servers: checking the installed version and applying the patches is the action explicitly requested by the manufacturer.
CISAconfirms active exploitation
On Friday, as reported by BleepingComputer, the US Cybersecurity and Infrastructure Security Agency (CISA) confirmed the exploitation of the vulnerability and included CVE-2026-97229 in itsKnown Exploited Vulnerabilities catalog(KEV). The agency asked the federal administrations involved to secure the systems by Sunday.
The inclusion in the KEV catalog is an important element: it is not just a theoretical possibility described in a technical bulletin, but a vulnerability for which actual exploitation has been found. The number of exposed instances monitored by Shadowserver also shows that the availability of a patch does not necessarily coincide with its adoption.
A second critical issue affects over 11,300 instances
Shadowserver also reported another significant exposure: beyond11,300 instancesvulnerable toCVE-2026-110264, about approx39,000GitLab installations observed daily. This vulnerability also affects the Regular Expression Compiler and could reportedly allow arbitrary code execution. However, this is a distinct identifier, which should not be confused with CVE-2026-97229.
During 2026, GitLab had already faced other critical issues: in January CVE-2026-0723, described as a high-severity flaw that allows you to bypass two-factor authentication, and in September CVE-2026-85706, related to the commits API and potentially usable to steal credentials and other secrets. The latter was also reported by CISA as being actively exploited, after watchTowr reported scans looking for vulnerable servers.
According to BleepingComputer's report, since November 2021 CISA has included six GitLab vulnerabilities in the catalog of actively exploited flaws; one was also used in ransomware attacks. The framework reinforces the need to keep self-managed instances up to date, without confusing different security issues and their respective exposure levels.
Editorial source consulted:BleepingComputer.


Commenti
Ancora nessun commento. Sii il primo a partecipare.